
An Enforcement Model That Provides Flexibility and Choice
The Nile Secure Network-as-a-Service (NaaS) delivers a flexible Zero Trust Fabric designed to allow customers to leverage the enforcement model of their choice, using either next-gen firewalls (on-premises, cloud or both) or Nile’s Trust Service; a complete Nile-delivered model, or a hybrid model leveraging both firewalls and Trust Service for policy enforcement. This ensures consistent, end-to-end enforcement across the environment—preserving existing tools, policies, and advanced security controls. Nile’s Zero Trust capabilities also provide a path forward that can eliminate third-party hosted firewalls.
By default, the Nile Zero Trust Fabric connects to upstream routers and firewalls over standard Ethernet, with routing handled through OSPF or BGP. This improves overall visibility, policy accuracy, and threat response without requiring customers to completely redesign enforcement requirements.
Nile and Your Firewall: Who Enforces What
Nile Enforces
Nile’s Core Trust Service natively provides secure access, per-device isolation and segmentation.
Customers can also choose to leverage Nile’s built-in microsegmentation, policy enforcement for north-south as well as specific local east-west flows—such as user-to-printer or segment-to-segment communication—eliminating unnecessary hairpinning through the firewall to improve performance metrics.
Nile’s Edge Service for WAN connectivity can also be used to eliminate local firewalls or SD-WAN appliances in some scenarios, such as in branch offices.
Your firewall enforces
A customer’s firewall can remain the enforcement point for north-south and selective east-west traffic. It's up to you.
An Any Firewall Model, Anywhere
Nile integrates cleanly with the firewall model a customer prefers—existing on-prem firewalls, SSE solutions, and Nile or third-party FWaaS—or a multi-tiered combination of them.
| Model | Vendors | Enforcement options |
|---|---|---|
| On-premises firewall | Palo Alto Networks, Check Point, Fortinet | Local firewall sees all traffic, including intra-segment traffic Hybrid: local firewall and Nile Trust Engine |
| FWaaS (cloud and on-prem) and SSE/SASE | Nile on-prem FWaaS: Palo Alto, Sophos Cloud security: Zscaler ZIA, Palo Alto Prisma, Microsoft Global Secure Access |
Cloud services see all traffic Hybrid: SSE/FWaaS and Nile Trust Engine |
| Multi-tiered | Local firewalls combined with edge firewall services or Nile enforcement | All enforcement via local or FWaaS (cloud, local, regional) Local or FWaaS and Nile Distributed enforcement: Nile and local or FWaaS All enforcement via Nile (east-west, north-south) |
On-Premises Firewalls
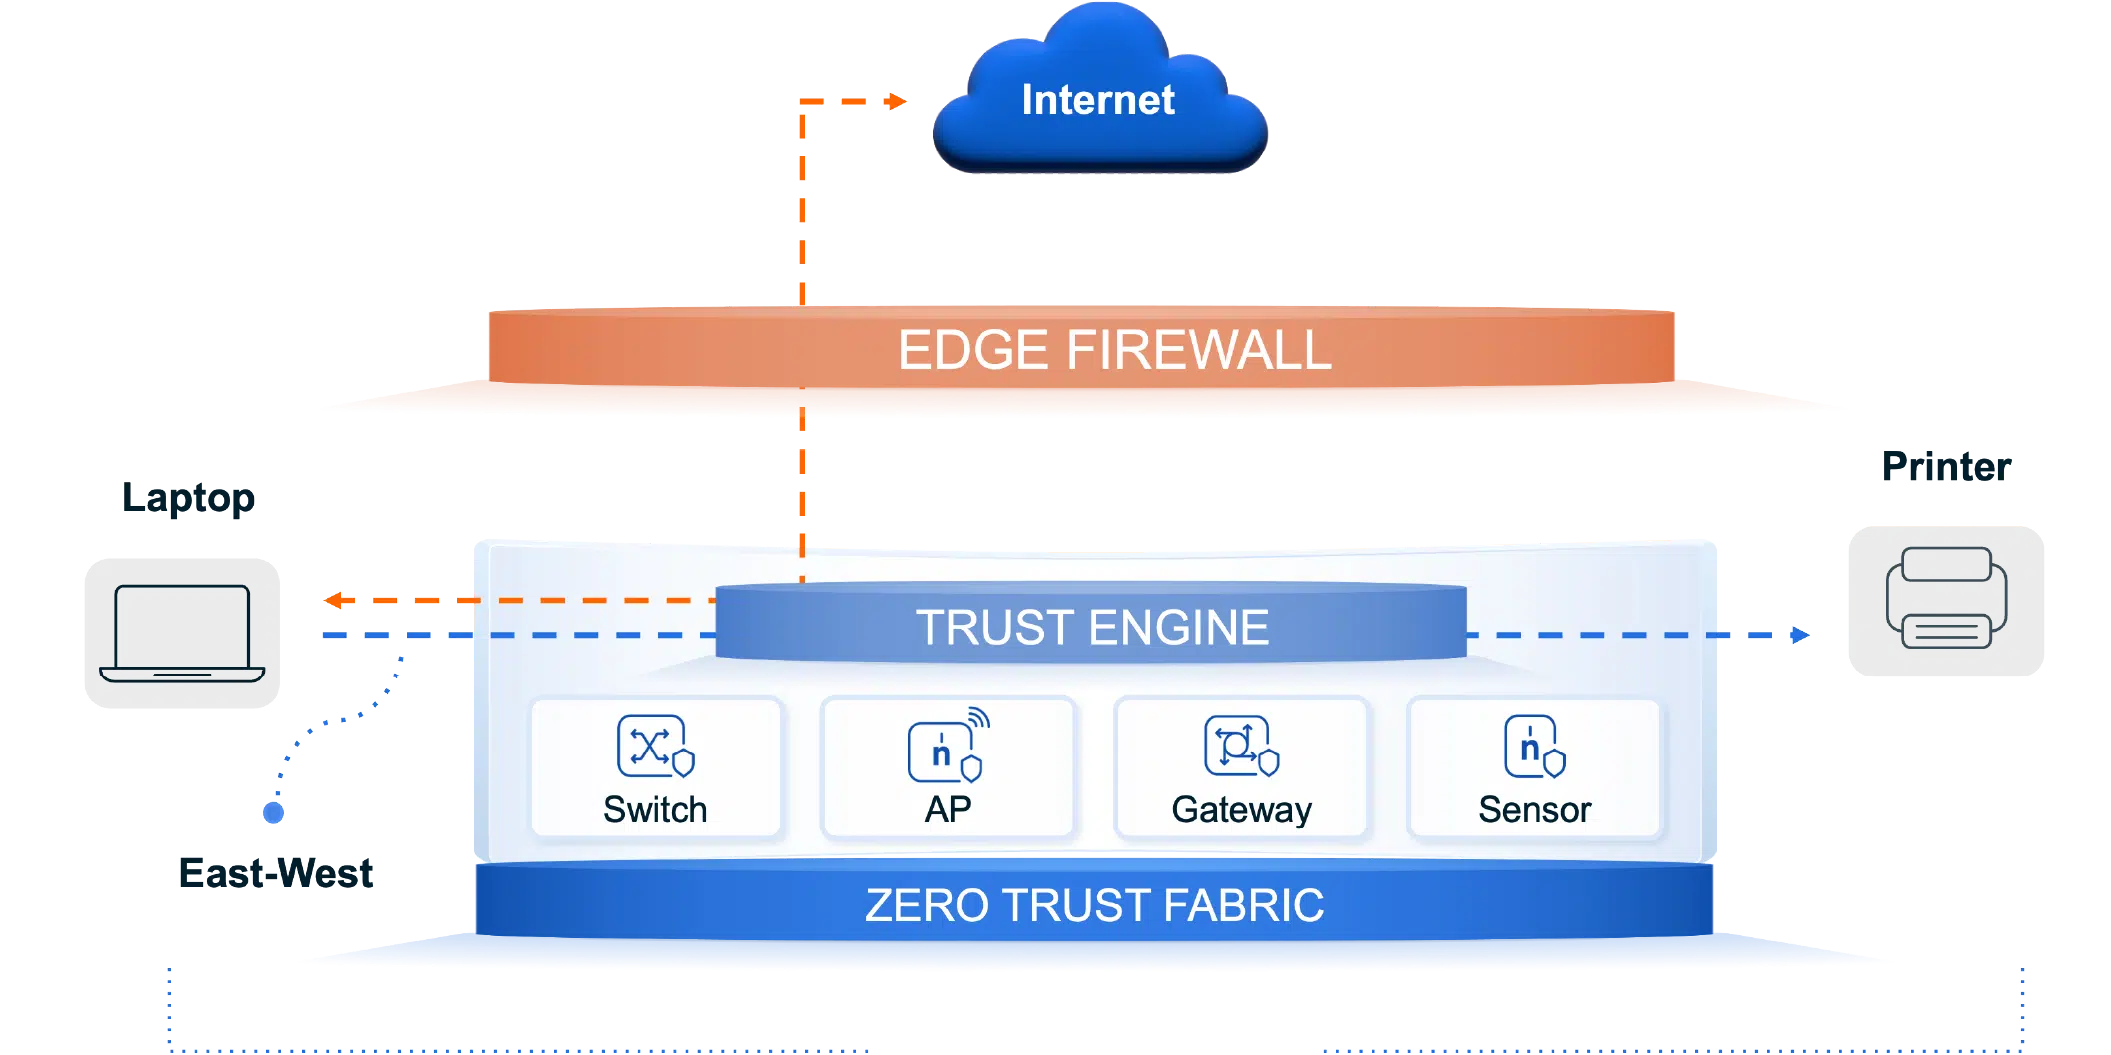
For on-premises, Nile works with leading edge firewalls from vendors such as Palo Alto Networks, Check Point or Fortinet.
How traffic flows
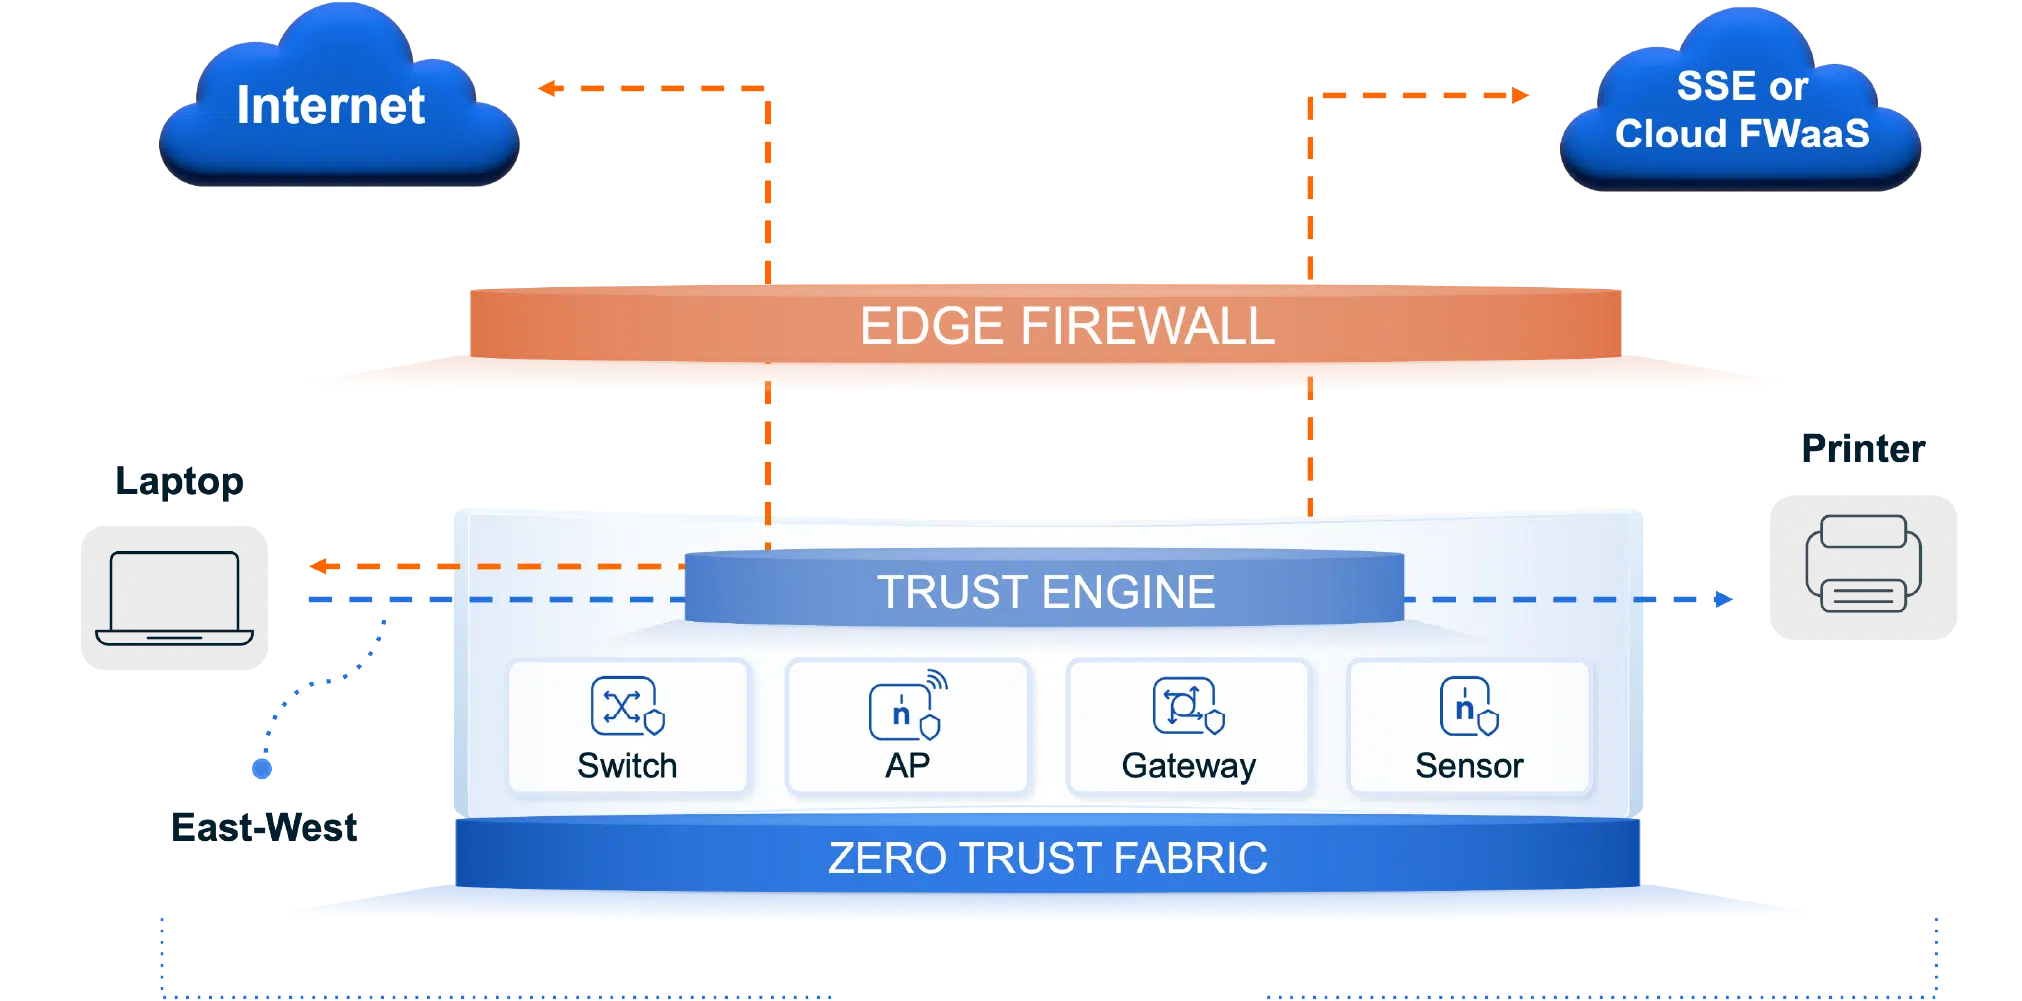
- The Nile Zero Trust Fabric (switch, access point, gateway and sensor) runs the Nile Trust Engine software module.
- East-west traffic from a device such as a laptop reaching a printer, passes through the Nile Trust Engine.
- North-south traffic passes from the Trust Engine up through the edge firewall to the Internet.
Firewall-as-a-Service and SSE/SASE
For those that prefer a more operationally flexible model, Nile supports the use of cloud or on-prem Firewall-as-a-Service (FWaaS) solutions. Customers can opt for their preferred vendor’s solution or take advantage of Nile’s on-prem FWaaS offering, which is a managed extension to the Nile Access Service. This includes Palo Alto and Sophos options.
Nile’s FWaaS includes onboarding, ISP connectivity, configuration management, health checks, updates, monitoring, and troubleshooting. This provides a single point of contact for network and firewall services—reducing vendors, handoffs, and operational silos that delay issue resolution.
Nile also supports regional cloud-based firewalls supported in private data centers or within SSE/SASE services. Nile seamlessly integrates with cloud security providers including Zscaler ZIA, Palo Alto Prisma, and Microsoft Global Secure Access. Full orchestration and monitoring of the secure tunnels created require no manual operations or intervention.
How traffic flows
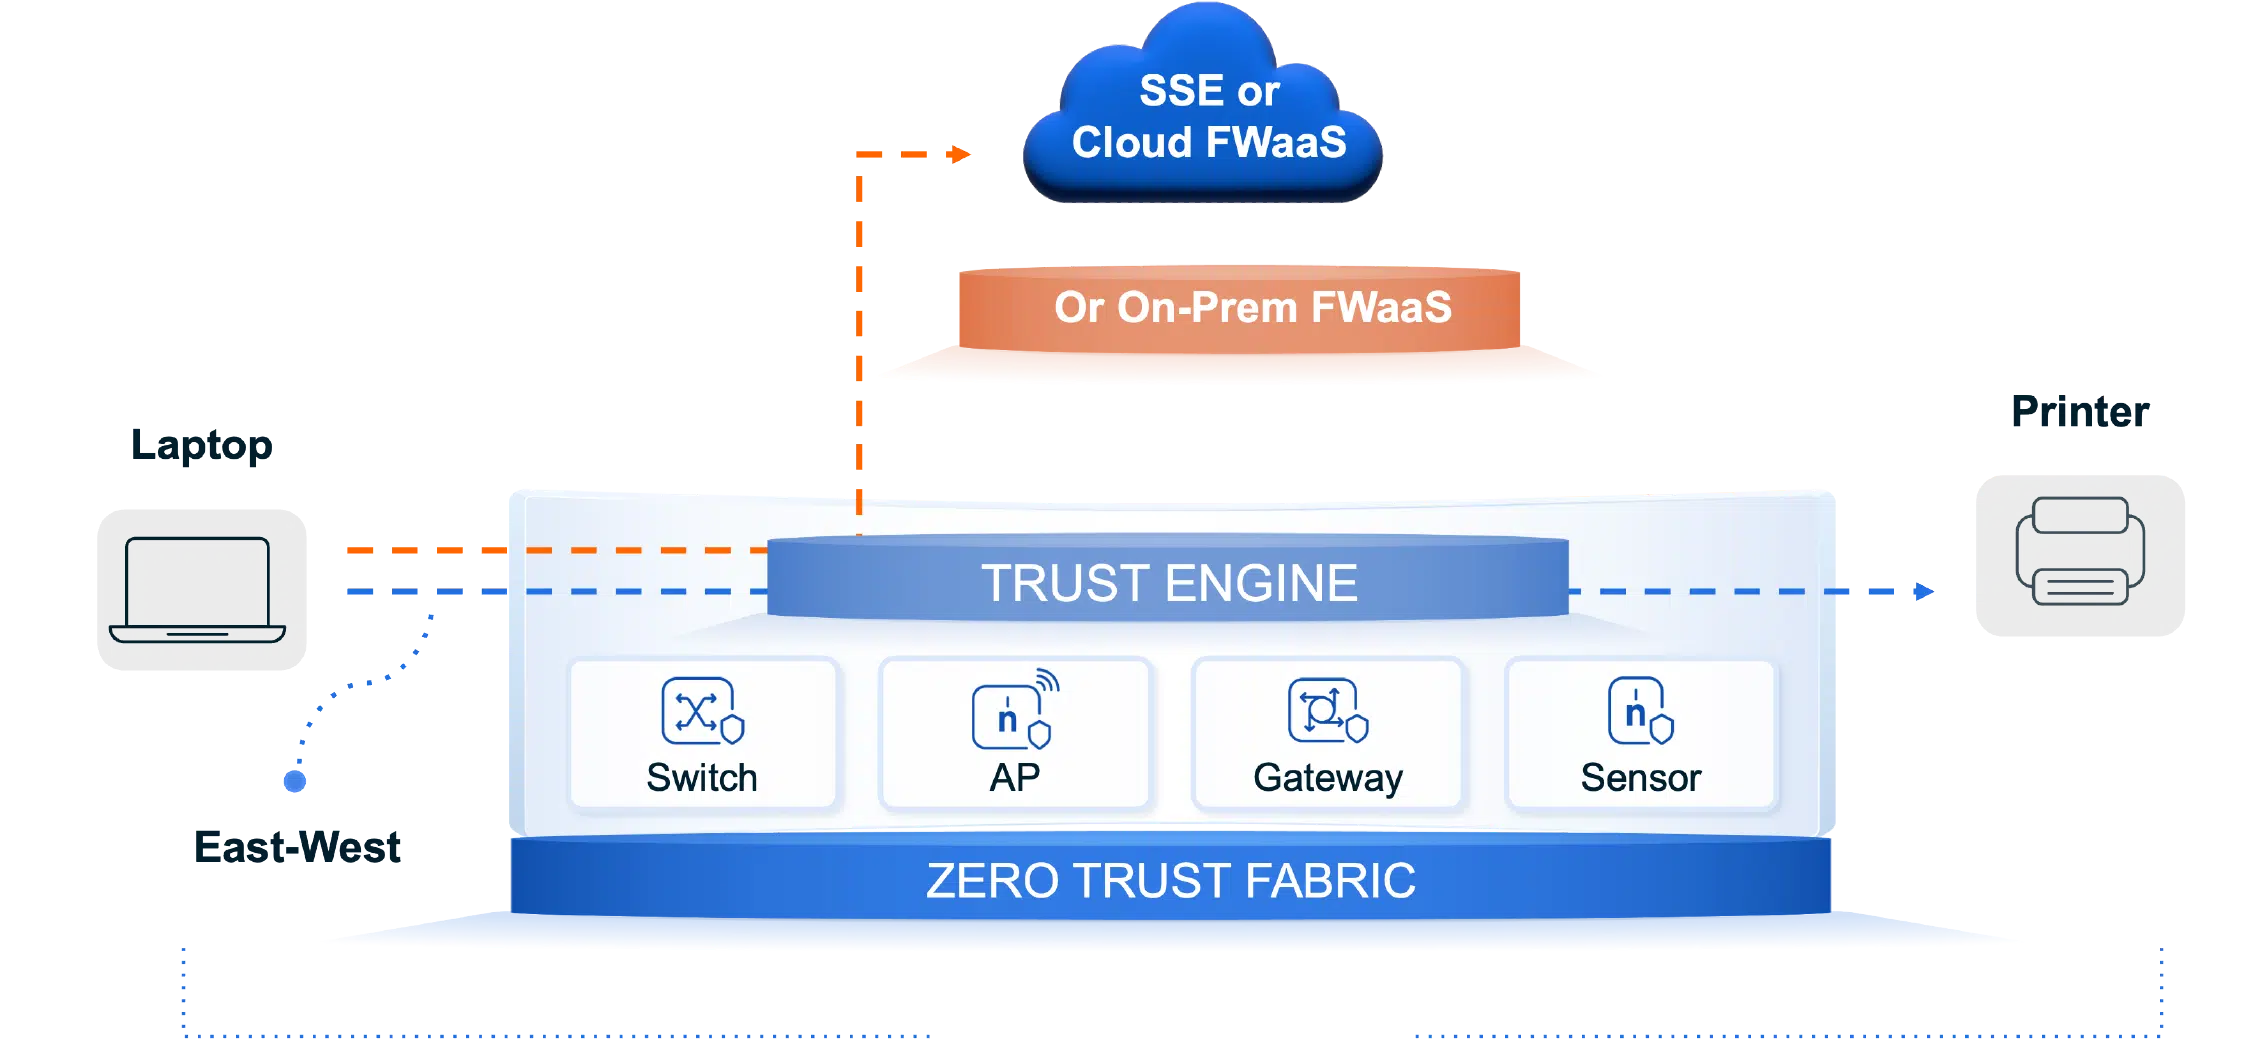
- East-west traffic, such as a laptop reaching a printer, passes through the Nile Trust Engine within the Zero Trust Fabric.
- North-south traffic passes from the Trust Engine to an SSE or cloud FWaaS service, or to an on-prem FWaaS.
Multi-Tiered Enforcement
A multi-tiered model allows organizations to combine local firewalls with edge firewall services or Nile enforcement where required. The following enforcement options are supported:
- All enforcement via local or FWaaS (cloud, local, regional)
- Local or FWaaS and Nile
- Distributed enforcement: Nile and local or FWaaS
- All enforcement via Nile (east-west, north-south)
How traffic flows
- East-west traffic, such as a laptop reaching a printer, passes through the Nile Trust Engine on the Zero Trust Fabric.
- North-south traffic can leave through the edge firewall to the Internet and to an SSE or cloud FWaaS service.
Again, Nile gives you the flexibility to use what you have or modernize
The result is a more flexible and modern security architecture that natively simplifies enforcement inside the LAN, and then integrates cleanly with whatever firewall model the customer prefers—existing on-prem firewalls, SSE solutions, and Nile or third-party FWaaS (can include regional data center firewall) solutions. This combination provides organizations with stronger security, simpler operations, and a more consistent Zero Trust experience from the campus to the branch, to the cloud.
FAQ
Frequently asked questions
Yes. Nile works with leading on-premises edge firewalls from vendors such as Palo Alto Networks, Check Point and Fortinet. The Nile Zero Trust Fabric connects to upstream routers and firewalls over standard Ethernet, with routing handled through OSPF or BGP.
Yes. Customers can choose Nile’s built-in policy enforcement for north-south traffic as well as specific local east-west flows, such as user-to-printer or segment-to-segment communication. This eliminates unnecessary hairpinning up and through the firewall to improve security measures and performance.
Nile integrates with cloud security providers including Zscaler ZIA, Palo Alto Prisma and Microsoft Global Secure Access. Nile provides full orchestration and monitoring of the secure tunnels, with no manual operations or intervention required.
Yes. Nile offers an on-prem FWaaS as a managed extension to the Nile Access Service, with Palo Alto and Sophos options. Nile FWaaS includes onboarding, ISP connectivity, configuration management, health checks, updates, monitoring and troubleshooting, giving a single point of contact for network and firewall services.
Nile’s Edge Service can be used to eliminate local firewalls or SD-WAN appliances in some scenarios, such as in branch offices. Gone are the extra licenses, power needs, support contracts and more.