The Secure Network you Need.
Delivered as-a-Service

Reimagining Network and Security Infrastructure and Operations for the Autonomous AI-Era

The Zero Trust foundation

Only authenticated users and devices connect. Nile minimizes blast radius through endpoint isolation and native, identity-based enforcement—enabling rapid containment without another security stack.

Reduce the network attack surface


Hardened by design

Verify identity-based access


Authenticate before access

Isolate every endpoint by default


Segment of one

Built-in enforcement and containment


Enforce and limit spread

No infrastructure to patch or maintain


Lifecycle included

Bottom Line

Leveraging dedicated network expertise maximizes operational uptime, protects internal resources, and drives strategic business growth by eliminating project delays and internal knowledge constraints.

The LAN is still the easiest path for lateral movement.

Users, unmanaged devices, IoT, OT, and critical systems all connect through the campus and branch network. Traditional networks were designed to connect everything — not to contain what happens when one thing is compromised.

Implicit trust

Shared networks and coarse segments give a compromised endpoint room to move.

Disparate controls

Access, segmentation, visibility, and enforcement live across separate products and teams.

Security that is hard to operate

Complex architecture and manual changes make strong policy difficult to sustain everywhere.

The easy button for a secure network.

Most organizations try to add Zero Trust onto a network that was not built for it. Nile starts with a secure foundation and delivers it ready to use — without creating another complex security project.

Reduce the attack surface

Hardened infrastructure removes unnecessary ways to access and expose the network.

Remove implicit trust

Every user and device is authenticated before it can connect, and is limited to access only what it requires.

Remove the tool sprawl

Access control, endpoint isolation, enforcement, containment, and operations are delivered together as one service.

For security and network teams: Nile replaces legacy network trust zones with endpoint-level isolation, identity-based policy, and enforcement built into the fabric—rather than asking teams to deploy and integrate separate NAC and segmentation-control layers.

Zero Trust built into the network. Not bolted onto it.

Nile unifies the wired and wireless fabric, access control, policy enforcement, and operations into one Secure NaaS experience.

1.

Limit the blast radius


Every endpoint starts protected by default. Communication is allowed only when it has a clear business purpose.

2.

Control every connection


Verify users and devices before connection, then grant only the access each one needs.

3.

Keep protection operational


Nile delivers, monitors, updates, and operates the service so protection stays current without adding lifecycle burden.

Security that does not create another infrastructure project.

Nile delivers the infrastructure, software, and operations together as a service—with Zero Trust security built in by default. Teams do not have to assemble, patch, and maintain a separate security stack around the network.

Legacy Network

Assemble and operate the stack

Nile Secure NaaS

Start from one secure foundation

Additional Resources

An Introduction to Modern NaaS

Webinar

An Introduction to Modern NaaS

In this session, we'll explore what a modern, secure NaaS truly means, and...

A Network Built for Security, Scale & Speed

Webinar

A Network Built for Security, Scale & Speed

Join us to discover how Nile’s secure Network-as-a-Service (NaaS)...

Nile Secure NaaS: An Innovative Alternative To Legacy Wired...

White paper

Nile Secure NaaS: An Innovative Alternative To Legacy Wired...

Frequently Asked Questions

What is Secure NaaS?

Simply put, Secure Network-as-a-Service is the network delivered by Nile as a service. This means as a customer, you do not need to procure the LAN connectivity equipment and operate the network for your branch or campus. Nile’s technology and service offerings take care of that. It’s also secure by design, architected on Zero Trust principles. Industry experts view this as a game-changer.

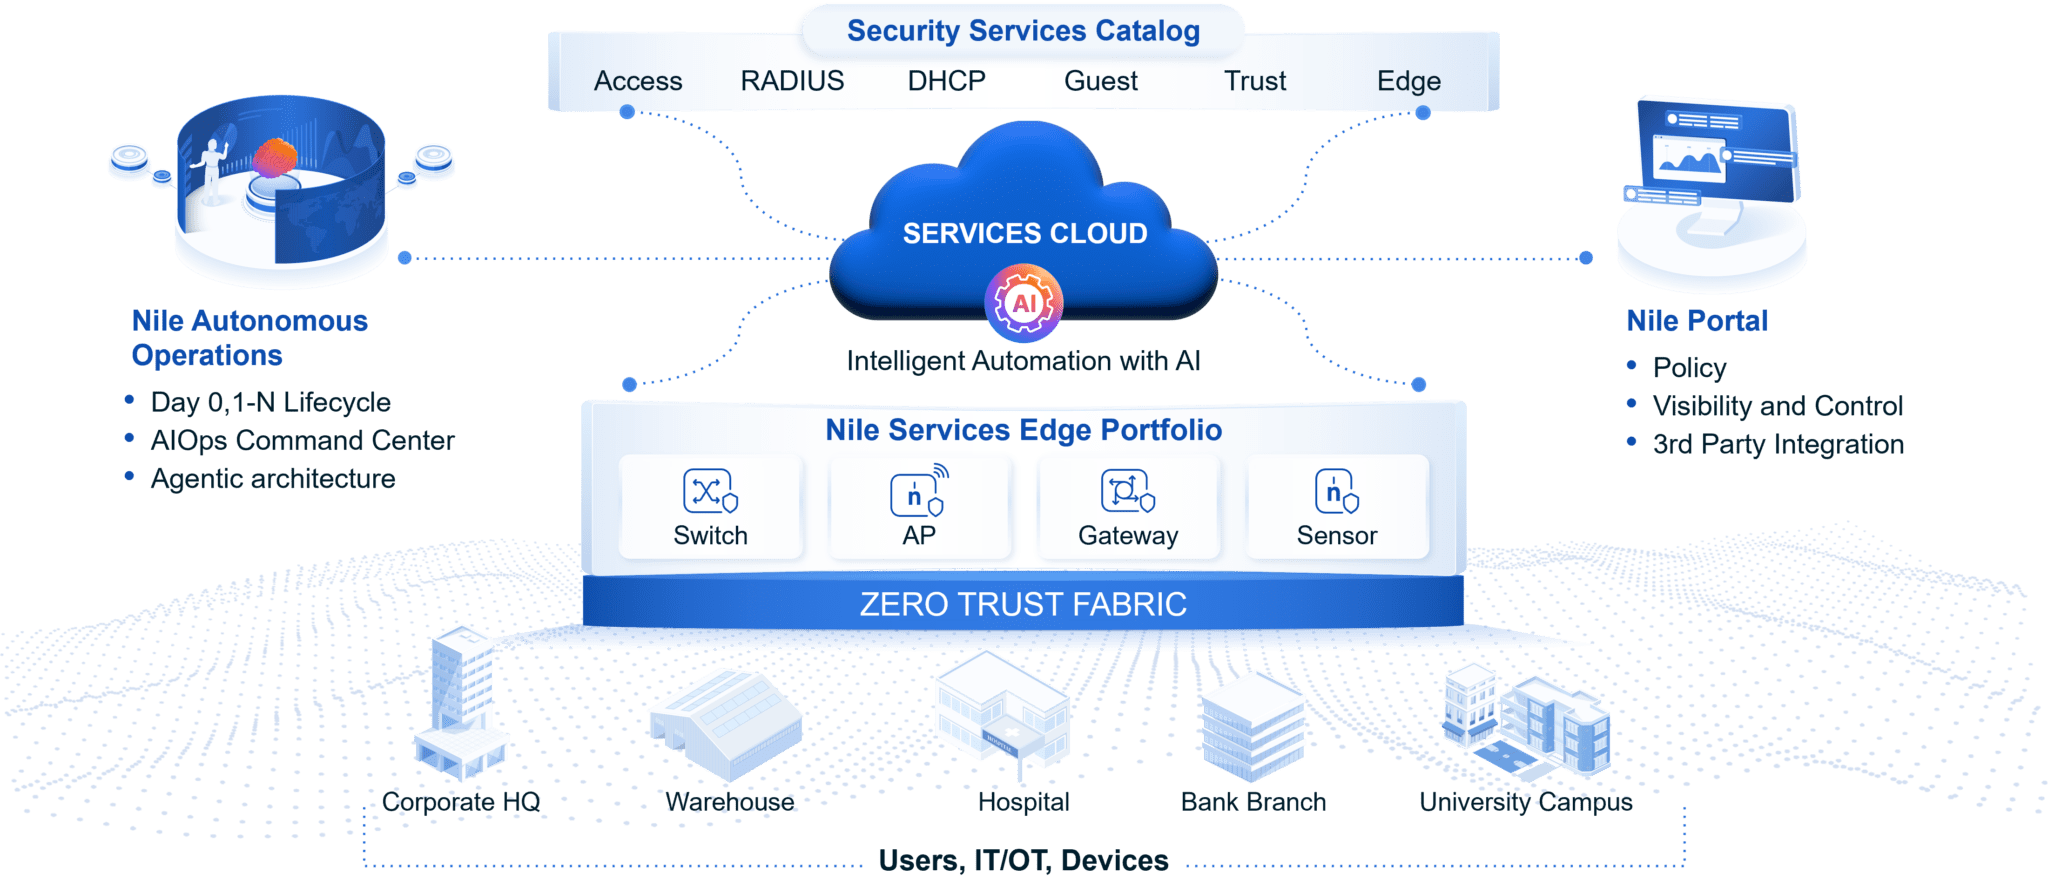
Nile is a technology pioneer and has built an advanced portfolio of enterprise-grade wired/wireless solutions for your local area network (LAN). It includes switches, access points, gateways and sensors functioning together as a zero-trust fabric. The Nile service cloud, its autonomous operations capabilities and Nile portal – all come together with artificial intelligence (AI) to deliver the as-a-Service offering.

Nile has received 60+ patents for its design, which are especially engineered to eliminate the massive complexity in legacy architectures. Nile’s technology is also tailored for service consumption, with Nile owning the technology and several of the operational services across the lifecycle unlike traditional box vendors who shop the box, and expect someone else to run operations, incurring additional cost and creating complex layers.

Customers purchase Nile’s service offering. Its patented technology is delivered as a part of the service offering. Nile’s service offering can be envisioned as three components:

  • Technology services: These are the primary services that customers purchase from the Nile services catalog. The Nile Access service is foundational for secure wired/wireless connectivity. All other services are add-on.
  • Lifecycle services: These are focused on the operational lifecycle of the network and tailored to meet the requirements of Day-0 (planning and design), Day-1 (implementation) and Day 2 (optimizing and operating the network) through its lifecycle.
  • Professional services: These are required for various aspects of service delivery where expert human engagement is required

Nile charges a subscription fee for its technology service offering. Most customers enter multi-year contracts based on the Nile value-add versus legacy pricing constructs and to simplify procurement hassles.

There may also be non-subscription fees for some charges that are one-time. For example, planning and design, or implementation will likely incur one-time fees specific to the requirements of a site or project. Professional services elements, service delivering shipping costs etc. are likely to have one-time non-recurring charges.

Yes, the Nile portfolio of switches, gateways, access points and sensors are included as part of the NaaS offering. Cabling, and other components that are requirements for implementation would be additional. Your Nile representative will provide details around the estimated cost structure.

No, Nile is not a managed service provider. Traditional MSPs manage the network built with someone else’s technology and hardware (typically an OEM). While they’re able to provide several services, for any hardware issues or advanced troubleshooting, they need to escalate them to the OEM. The OEM has limited visibility into the deployment, and this can belabor resolution. This can lead to “blind spots”, downtime and cost escalations. Nile is both the technology vendor (OEM) and the as-a-service provider allowing deep visibility and expedited resolution on an end-to-end basis. It also allows Nile to offer an end-to-end SLA that’s not just based on uptime, but on service experience.

Yes, Nile can work with an incumbent MSP (or Telco) or be offered as a service through them. Many of them enjoy the benefits of the ease of Nile service offering as it minimizes truck rolls for them and helps their customers, while positively impacting their bottomline.

Yes, Nile is highly suited for distributed deployments in a campus, city, country or across the globe. Normally customers with distributed locations struggle to deal with the operational complexity. Even large enterprises with do-it-yourself (DIY) teams are challenged with heterogenous distributed sites. If the management it outsourced to multiple MSPs across cities or countries, it can amplify complexity and cost, as they may have non-standard operational models. All this creates friction and further impedes business velocity and change management. Nile can deliver a standardized operational model with end-to-end visibility across all sites regardless of their location, if the sites are powered by Nile technology.

Yes, Nile is very partner friendly. It adopts a partner-first, customer-first model. Channel partners love Nile technology, as it delivers transformative benefits to their customers, while positively impacting their margins. Fewer truck rolls, faster service activation and change management, deep visibility and proactive resolution of incidents through Nile’s autonomous operations capabilities – all help contribute to better margins and customer loyalty.

Nile Secure NaaS augments IT staff and helps boost their productivity. Most organizations struggle with Lean IT that is challenged to do more with less, often causing burnout. Manual configurations at scale can also cause inadvertent errors leading to security vulnerabilities and other incidents compromising an organization. If operations are outsourced to one or more MSPs, the cost escalations can grow, with non-standard instrumentation and operational models further requiring IT to actively manage changes. Nile simplifies all this through its transformative architecture, that has eliminated legacy protocols leading to radical operational simplicity and security. This allows IT teams to drive more impact, shifting focus from the mundane to deliver on transformational initiatives for the organization. NetSec/ IT teams love the Nile experience as it empowers them to deliver greater impact while reducing burnout. C-level executives can scale the IT impact even on tight headcount and operational budgets with Nile.

Nile’s unique Secure NaaS model offers greater security, unparalleled simplicity, faster change management and significant cost savings while factoring in how much an organization spends on technology, service delivery and operations over the lifecycle compared to the traditional approach. All this reduces risk, increases organizational velocity and delivers a superior user experience – elevating IT’s impact.

  • For CIOs – Nile helps accelerate transformation initiatives with faster change management despite lean IT resources and lean budgets, while delivering a stellar end-user experience.
  • For CISOs – Nile increases security and lowers risk, making it easier to drive compliance and reduce breaches.
  • For CFOs – Nile’s Opex model brings predictability of costs, while delivering 30-50% cost savings over the lifecycle removing the need for unpredictable CAPEX spikes every 5 years.
  • For Procurement – Nile vastly simplifies the need for multiple licenses, vendors, operators etc, and simplifies cost structure and accountability. Managing expansion and change order also becomes vastly simpler.
  • For NetSec operators – IT teams responsible to administer and deliver networking, security and user experience in the LAN, benefit from deeper end-to-end visibility, reduced tickets etc. and the ability to drive strategic impact faster without budget over runs.

Make the network your strongest line of defense.

See how Nile can help contain threats, simplify access control, and deliver a secure network experience across every campus and branch.